Subscribe:
Showing posts with label Wildcard-SSL-Certificate. Show all posts

Sunday, 25 September 2011

Lync Deskphones and Wildcard Certificates


A critical component of any Lync deployment is the deskphone.  While some users may be comfortable with using a headset/PC combo as their primary telephony interface, I've found that most users still prefer a deskphone.

However, getting a Lync deskphone to work with Lync can be a bit tricky if you aren't diligent about following Microsoft best-practices to the letter.  You may have a Lync environment that works perfectly well for computer-based Lync clients, but you may come across various connectivity issues when you plug in a Lync deskphone that does presence and Exchange calendaring. 

I recently came across a client who were having Exchange connectivity issues with their Polycom CX600 phones.  The Polycom CX600 is likely the most popular Lync deskphone. It provides a very slick interface into Lync and Exchange so you can see your presence, contacts and upcoming meeting information. It is also very cost-effective compared to other similar products.

When users signed into Lync on their CX600 (either via keypad or USB-PC integration), they were soon presented with the following error:
 
Microsoft Exchange integration unavailable.  Connection to Exchange is unavailable due to invalid network credentials.
The CX600 uses Exchange Web Services (EWS) and autodiscover to find the connection to Exchange.  If there are issues with either service, it will pretty much guarantee that the CX600 won't connect.  I verified that both EWS and autodiscover were working properly.

When I reviewed the certificate loaded on the Exchange Client Access Server, I saw that the common name (CN) was set to their public domain (ie. contoso.com).  The Subject Alternate Names (SAN) included all the required names.  Microsoft Lync documentation recommends that you do not use certificates with the CN set to a wildcard domain name.  You CAN use wildcards in the SAN, but the CN really should be a valid name.  In this case contoso.com is the same as *.contoso.com. 

The client replaced the certificate with one whose CN matched the externally accessible name of the CAS server (owa.contoso.com) as reported by Exchange.  They issued an IISReset, restarted the CX600 and the error went away.  They now have full connectivity to Exchange via the CX600.

I've seen variations on this many times on both Exchange and Lync.  If you're only using Lync PC clients, you may never notice any issues, but as soon as you bring deskphones and even mobile phones into the mix, these sort of things often come up. 

So as a general rule, if you're creating certificates for Lync or Exchange, 
DON'T use a Wildcard SSL as the first name.

Monday, 5 September 2011

Get Wildcard SSL Certificate @ Discount Price & secure your multiple sub domains with single wildcard SSL


Questions? Call
727-388-4240

Wildcard SSL- thesslstore.com offer Wildcard SSL certificate at best prices ever. Secure your multiple sub domains with single wild card ssl certificate.


Get Wildcard SSL Certificate @ Discount Price

Wildcard SSL Certificates:-
  1. GeoTrust True BusinessID Wildcard
  2. If you're looking to secure multiple websites with one server certificate, GeoTrust True BusinessID Wildcard SSL Certificate is the easy, affordable solution. GeoTrust True BusinessID Wildcard SSL Certificate is an ideal solution if you need to secure multiple fully qualified domains that share the same base domain name and reside on the same physical server and share the same second level domain name.
  3. Thawte Wildcard SSL
  4. Thawte Wildcard SSL is an easy, affordable solution if you need to secure multiple fully qualified domains that share the same base domain name, reside on the same physical server, and share the same second level domain name.
  5. RapidSSL Wildcard
  6. RapidSSL Wildcard SSL Certificates allows you to secure unlimited number of sub domains. RapidSSL is industry standard 128 / 256 bit single root SSL certificate. RapidSSL certificates have browser recognition of around 99% including IE 5.01+, Netscape 4.7+ and Mozilla 1+ browsers and many other browsers.

Get Wildcard SSL Certificate @ Discount Price

URL:- https://www.thesslstore.com/wildcardssl-certificates.aspx

Sunday, 4 September 2011

Google Wildcard SSL Certificate Stolen and Publicly Posted


Hackers have gained access to and made publicly available a digital SSL Certificate for any Google website.

This means that anyone with this certificate could perform a "man-in-the-middle" attack to target Gmail users, Google Plus users, or any other users using Google's online services.

If a hacker is going to steal a certificate, this is definitely the one to get since its considered a wildcard certificate - good for any .Google.com domain. All a hacker has to do is present a fake web site which looks like Google, by poising of DNS or other means, and then present the stolen certificate. Because the certificate is legitimate for any Google.com domain the users would have no warning at all that anything is amiss. Then the attacker could easily steal your login credentials gaining access to all of your Google services.

This specific certificate stolen was issued by DigiNotar, a Dutch-based certificate authority (CA). It's not known if DigiNotar was hacked or if the certificate was stolen by other means.

"The certificate authority system was created decades ago in an era when the biggest on-line security concern was thought to be protecting users from having their credit card numbers intercepted by petty criminals," said the Electronic Frontier Foundation a digital rights group based in the United States. "Today internet users rely on this system to protect their privacy against nation-states. We doubt it can bear this burden."

There has already been reports of Iranian web users being attacked by using the stolen certificate but Google Chrome was already updated to thwart the attack. Google has also already revoked the certificate so that it no longer works.

Google spoke in a statement yesterday that they were "pleased that the security measures in Chrome protected the user and brought this attack to the public's attention. While we investigate, we plan to block any sites whose certificates were signed by DigiNotar." 

Tuesday, 23 August 2011

Increase your Website Sales & Security by using GeoTrust QuickSSL Premium Certificate

In today's world of rapidly expanding technology all people are using e-media for buying or selling products and services. Thus, e-commerce is proved to be an important component of business strategy any form of business transaction in which the parties interact electronically rather than by physical exchanges or direct physical contact is known as e-commerce. In simple words, it is an act of buying or selling on internet or other communication networks. The development and acceptance of online shopping, telephone banking, credit cards, data mining, data warehousing, enterprise resource planning (ERP) systems and World Wide Web (Internet) are the revolutionary components of electronic commerce.

But still millions of people are facing security problem for sharing them confidential data on I-world and that’s why they will think twice or leave the websites which does not carries security protocols. That’s why If your site is selling products to the public, it is crucial to develop trust with your users by securing your website with SSL Certificate. GeoTrust QuickSSL Premium certificate is the least pricey option for a valid and relevant SSL certificate. When you display GeoTrust SSL certificate, you inform your users that you value their information and it’s secure. GeoTrust SSL Premium certificate also build the trust to end users that his or her data will not disclose to anyone and this faith creating valuable relation & trust. By this way your online sale will increase exponentially.

GeoTrust QuickSSL Premium certificates are one of the quickest ways for you to start protecting your website online transactions and applications.

Thesslstore.com is one of the largest resellers SSL store in world which offerSSL Certificate for Websites in worldwide including Money Back Guarantee, Price Match Guarantee, Customer Royalty Program, and 24 X 7 hrs Platinum Support System via various communications such as email, live chat, and telephone. So secure your fully qualified domain name, including both the NON-WWW and WWW details, with the GeoTrust QuickSSL Premium now at very affordable cost.

How SSL Certificate Work? Why you should include In the E-commerce Web Design SSL?

As a web designer, it is important to know about SSL certificates. How SSL certificate work? Read on to learn more about SSL Certificates and why it is important to include the design of your ecommerce site.

How SSL certificate work?

To send the form to the network (such as credit application), the browser must first request a protected page, the web server. Subsequently, the server sends the public key certificate for an SSL site. The browser will then ensure that the certificate is valid and reliable by the party.

Once verified, the browser uses a public key to create and encrypt a random symmetric encryption key. Then sent to a Web server with the data in encrypted form and the https URL. Once received, the web server uses a private key to decrypt the symmetric encryption. Decrypts the symmetric key and the form data and URL.

Required format and data online (HTML) is sent to the Web server encrypted with a symmetric key. The browser then decrypts the data and documents using a symmetric key and displays the information to the recipient

Why should you use SSL in your website?

You should add SSL Certificates for websites if they plan the early stages of online stores where customers can buy products. Financial information (like credit cards) and other confidential information from online forms. Without SSL, the data is easily intercepted and stolen by people who are "packet sniffing" using software that can eavesdrop on your network. Unsecure websites can be identified by the “http” in their URL. In general, these types of sites are generally informational in nature and do not have interactive online forms. Deemed secure SSL sites have "https" in their URL, and will have a padlock icon at the bottom right of the page. If you sell items and an online form without the "https", you will not get many customers.

Online forms deemed secure SSL sites have "https" in their URL, and will have a padlock icon at the bottom right of the page. If you sell items and an online form without the "https", you will not get many customers.

A good understanding of how SSL certificates work is important because sensitive financial information can be compromised and stolen. When creating a secure ecommerce website, it is essential to set during the early stages of design for the safety of clients and owners of e-commerce site.

Tuesday, 9 August 2011

Taking Advantage of Wildcard Certificates

If you've done some SSL Certificate research, you would notice that SSL providers only allow one domain to use one SSL certificate. This means that buying an SSL certificate for example dot com will not give you SSL security for www.example dot com or secure.example dot com. Most people can get away with only one SSL certificate, but what about those who use several domain names? Here's an example of a website that uses several domain names: shop.bigbusiness dot com, secure.bigbusiness dot com, buy.bigbusiness dot com, and mail.bigbusiness dot com.

You may buy SSL certificates for every additional subdomain on your website, but costs will significantly increase if you need certificates for four or more subdomains. Fortunately, you have the option to go for wildcard certificates that allow you to use one SSL certificate on an unlimited number of subdomains.

Wildcard? What's that?

You might be curious what "wildcard" means in "wildcard certificate". In computer terminology, a wildcard is basically a sybol, usually an asterisk (*), what stands to be replaced by another character or string. Very simply, an asterisk may mean any word. For example, *.example dot com refers to all subdomains of example dot com like mail.example dot com, secure.example dot com, news.example dot com, etc.

The "Common Name" field in an SSL certificate indicates the domain in which the certificate will be used. Wildcard certificates are basically certificates with wildcards in the Common Name, like *. bigbusiness dot com. If, in the future, you choose to get a wildcard certificate, you will be asked to supply the Common Name.

Good Things About Wildcard Certificates

Purchasing just one Wildcard Certificate for all your subdomains will obviously save you a lot of money. A typical SSL certificate costs about $150 which is fine if you only use a few subdomains, but with five subdomains, you’ll need to shell out $750. Think about how much money you can save if, let's say, you own a website with 10 subdomains needing SSL security. That's already $1,500. Comparing that to wildcard certificates that only cost $600 each, you save $900. The websites of big companies will sometimes need SSL on over 30 subdomains.

Manageability is another benefit to using wildcard certificates. It's not easy to purchase, set up, and then renew annually a number of SSL certificates. It's an extremely error-prone task for a single person to manage so many SSL certificates all at once. Fixing those errors will cost you money. On the otherhand, think about worrying about just a single wildcard certificate. Managing just one certificate is a much simpler task. Errors, in this case, become rare.

The Bad Things about Wildcard Certificates

Using wildcard certificates does have some drawbacks. The first thing that experts will point out is problems with security. Big websites are usually run by multiple servers, and by sharing one wildcard certificate, they share a single private decryption key. This means that if someone manages to compromise one of your servers and retrieve the decryption key, every subdomain on every server that uses the same certificate is also compromised.

All subdomains will cease to work if the wildcard certificate is revoked for any reason. Until you fix the wildcard certificate or get individual SSL certificates for each subdomain, you may have to put your website on down time.

The last thing you should know is that Extended Verification (EV) does not work with wildcard certificates. What is EV in the first place? It's a set of stringent rules that certificate providers use when approving applications for SSL certificates. EV was meant to increase public confidence in SSL. Wildcards in the Common Name are not allowed by EV guidelines. The green address bar feature only works in EV SSL Certificate, so you don't get that feature with wildcard certificates.

Sunday, 7 August 2011

The Variances Among Wildcard SSL And EV SSL To Safe E-Commerce

Next you want to make sure that the provider you come to a decision to host your domains at features excellent purchaser help. These days you will need to only go with one that offers a toll-absolutely free amount furthermore 24/seven support.

If you are a Microsoft Front web page consumer, the Inexpensive Domain Identify and Internet Hosting service you choose will need to offer you Front Web page Extensions. If you presently know how to FTP that’s terrific. You’ll by now know how to get your webpage reside on the internet. However if you you should not, you will want to go with a service that gives a Free Internet site Builder and Web page Templates. Internet site Templates will help you save you from owning to go out and employ a website designer.

Make confident the Low-priced Domain Name and Web site Hosting support you pick presents Global Domain Names Help if you have a domain with a region particular extension like .au or .br or .ch for instance. Ultimately it’s often a good thing to be able to personalize your error pages so find a support that provides this characteristic as properly. And final but not minimum, get one for underneath $ten.00 per month. Yeah I’ve heard of a couple of for only a several dollars per month, but they are no superior and have no where by close to the characteristics you will need as your firm grows its upcoming online presence.

Diverse companies supply various cost for registering domain, down below we will speak about the components which will impact the selling price of domain sign up and where to uncover a best amount for it.

Critical Thing in Registering Domain

You have no want to shell out $35 per calendar year to get a domain identify, some really excellent and reputed providers will sale you a domain with pretty lower amount. You will need to spend an annual price to the domain sign up corporation, so never forget about to renew your domain every yr.

The price tag of domain is varied based mostly on the domain extensions you sign-up. For domain extension like .com, .web, it will charge you only about $seven every single year, but for “mobi” domain extension, you may well have to spend out $20 for each 12 months. Besides the domain extension, the domain sign-up corporation from different provider will consult for distinctive sign-up payment for the state level domainextension. This kind of as, you will get a minimal cost as ?one.99 from 1&amp1 United kingdom (which is a Uk firm) for domain extension “co.uk” (United kingdom place level domain extension), and a USA corporation may necessitate more for this domain extension.

When registering domain, you will usually be asked about the alternative for “Domain Privacy Protect”, this solution will allow for you to choose not to open your register facts so that people today won’t discover who unique the web web site through whois. In most circumstances, I would like to endorse this possibility for man or women, but for the provider, it isn’t going to make sensation to cover the sign up info due to the fact you want additional people to know who unique this web-site.

Source URL:-http://worldvillage.com/octaviowells38-bryon-floyd

Wednesday, 3 August 2011

Alternatives to Wildcard SSL


When browsing the Internet, you may notice that some websites include a padlock next to the URL. This signifies that that website is secured by an SSL certificate, which is short for "Secure Socket Layer." The certificates are used by website developers to encrypt data transmitted on websites. For example, you should be using a SSL Certificate if you will receive customer's credit card or other sensitive information on your website. There are several alternatives to Wildcard SSL.

  1. GoDaddy SSL Certificates

    • GoDaddy offers standard and premium SSL certificates that are used to secure websites. According to the site's description of the two options, the standard certificate validates domain ownership, and secures the site "within minutes." Unlike the premium version, the standard version does not offer a green address bar, which alerts visitors that the site is secure. However, it does offer the padlock icon for covered domains.

    Symantec SSL Certificates

    • Symantec offers more than 70 percent of the SSL certificates on the world's top 1,000 domains. Symentac's offers SSL certificates through its VeriSign service. It also includes daily malware scanning, ensuring that visitors machines will not be infected by visiting your site. Finally, the VeriSign SSL certificates offers the green address bar and the padlock.

    GeoTrust

    • GeoTrust is another option for SSL certificates. The website lists six different SSL certificate options. They are the True BusinessID, True Business ID with EV SSL, True BusinessID Wildcard, UC/SAN and GeoTrust QuickSSL Premium. Each certificate option offers varied features. For example, the True BusinessID certificate offers full authentication and a GeoTrust site seal, while the True BusinessID with Extended Validation offers the same features with an extended warranty.

    Network Solutions

    • Network Solutions also offers five different SSL certificate options: Limited Verification, Basic and Advanced Business/Organization Verification, along with Wildcard SSL Certificate and Extended Verification. The major differences between these are the degree of warranty for each package, along with the difference in organization sizes. For example, large organizations may prefer the "Wildcard" or the "Extended Verification," which both include a larger warranty than the smaller packages. Each also offers the browser padlock and a site seal.

Monday, 1 August 2011

The Risks In Wildcard Certificates


They may not be real-world problems, but Wildcard Certificate have some definite theoretical problems. But they can be so much cheaper that users will buy them anyway.


The imperative to use SSL, for web authentication and encryption or VPNs, is reasonably universal. Competition has driven prices of certificates down over the years to the point where you can get conventional SSL certificates from reputable vendors for well under $100 per year.

Another product gaining popularity due to competition is the Wildcard SSL Certificate. A conventional certificate works on a single domain, e.g. www.foo.com. A wildcard certificate protects all subdomains of a domain subject to the use of wildcard characters in the name. So a wildcard certificate for *.foo.com protects www.foo.com, bar.foo.com, mail.foo.com, chasephish.foo.com, and so on.

I have received many notes from vendors about them, both as press and as a prospective customer. Most CAs (certificate authorities) clearly see them as a way to grow markets. If you've got a lot of domains you can save a lot of money with a wildcard certificate relative to buying individual certificates for them, but not from all vendors. VeriSign, the 800 lb. gorilla in the CA room, prices wildcard certs by the domain being protected, so that they don't save much, if any money outright.

There is still a potential to save in convenience of administration with a wildcard certificate. But there are real downsides to wildcard certificates. When things go wrong the convenience may evaporate quickly. The VeriSign site lists their take on the disadvantages of wildcard certs:
  • Security: If one server or sub-domain is compromised, all sub-domains may be compromised.
  • Management: If the wildcard certificate needs to be revoked, all sub-domains will need a new certificate.
  • Compatibility: Wildcard certificates may not work seamlessly with older server-client configurations.
  • Protection: VeriSign Wildcard SSL Certificate are not protected by NetSure extended warranty.

I hope it doesn't need to be said that VeriSign, as the dominant market player, has an interest in prices remaining high, so take their advice on wildcards in that light. The last point is VeriSign saying that wildcards get a lesser level of service from them, so that's not a problem inherent in the technology, but the other 3 points are reasonable generally.

Tuesday, 26 July 2011

Protect Your Entire Site With The Same SSL Certificate


The Thawte Wildcard SSL Certificate allows you to secure unlimited subdomains of your main domain with a single Certificate. For example, if you have the domain abc.com, any number of subdomains will be protected by this certificate: mail.abc.com, store.abc.com, etc.. You will not have to buy separate Certificates for each new subdomain as is the case with standard certificates. This solution is ideal if you use SSL for multiple subdomains – only one certificate to install, and in many cases it is more cost-effective. Please note that all subdomains must be on the same Server.

Thawte Wildcard SSL Certificates may use an IP address to all secondary domain names. The same certificate can be used to secure all subdomains associated with a domain name, sharing one IP for all subsequent years. You can configure name based virtual hosts instead of machines.

Reasons for Choosing the Thawte Wildcard SSL Certificate:

• Encryption strength from 40 to 256 bits, according to the ability of browsers clients. 
• Issue in 2 business days, depending on the fulfillment of the requirements by the applicant.
• The ubiquity is the highest available in the browser market.
• High standards of validation, through the intervention of a trusted third party such as Thawte, which guarantees the authenticity of your company and website ownership for Certification. 
• Rigorous Verification and authentication procedures integrated (domain name and identity certificate validation). The prestige of Certificate Authority (CA) authorization. 
• Protocol Secure Socket Layer (SSL), maintaining privacy of messages exchanged between the web Server and its users. 
• Recertification without limit during the lifetime of the Certificate.
• High-strength encryption technology and high reliability of the site signature to protect your transactions.

Read more:-http://www.hostreview.com/news/110726-protect-your-entire-site-with-the-same-ssl-certificate#ixzz1TCIg1zf7

Monday, 11 July 2011

Wildcard SSL Certificates: What Is It?


What Is It?

A Wildcard SSL Certificate helps enable SSL encryption on multiple sub-domains using a single certificate as long as the domains are controlled by the same organization and share the same second-level domain name. For example, a Wildcard certificate issued to Company ABC using the Common Name (“*.CompanyABC.com”) may be used to secure the following domains:
  • login.companyabc.com
  • payment.companyabc.com
  • support.companyabc.com
How VeriSign Can Help?

Ask your VeriSign sales contact about Wildcard SSL Certificates. A common, high-level standard of security across all types of configurations is better achieved when you do not share or copy certificates among servers. Limitations of using Wildcard SSL Certificates include:
  • Security: If one server or sub-domain is compromised, all sub-domains may be compromised.
  • Management: If the wildcard certificate needs to be revoked, all sub-domains will need a new certificate.
  • Compatibility: Wildcard certificates may not work seamlessly with older server-client configurations.
  • Protection: VeriSign Wildcard SSL Certificates are not protected by NetSure extended warranty.

Sunday, 10 July 2011

Phishing Sites Explode on the Web

Online criminals are thriving even in the face of new automated defenses.


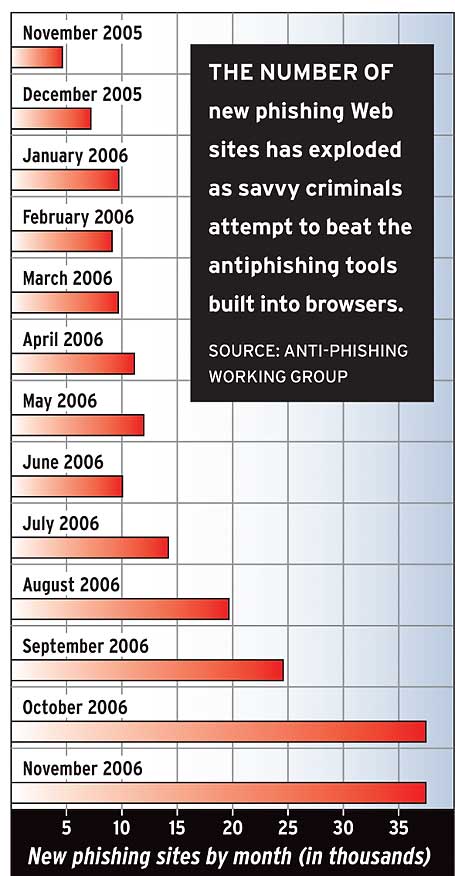
Think the new built-in phishing filters in Internet Explorer 7 and Firefox 2 will protect your private data? Think again. The number of sites devoted to phishing skyrocketed last year, and the number of Americans taken in by phishing schemes has nearly doubled. In November 2006, the last month for which data is available, the Anti-Phishing Working Group found 37,439 new sites, up an astounding 709 percent from the 4630 sites in November of 2005. (Click on the "Image Enlargement" icon above to see the chart showing this trend.)
Last October, both Mozilla and Microsoft released new versions of their browsers that use blacklists to block access to known phishing sites. In response, resourceful phishes are flooding new fake Web sites onto the Internet too quickly for them all to be shut down or blacklisted.
The alarming ease, with which the fraudsters changed course, plus other new phishing tactics, makes some security experts say that phishes have the upper hand in the war against online fraud.
"Ultimately," warns Zulfikar Ramzan, who is a senior principal researcher with Symantec's Security Response Group, "technologies that rely heavily on blacklists are going to be useless."
Easy Phishing
According to RSA, a security vendor, hackers in January started selling a phishing kit that lets criminals set up very convincing fake Web sites with little effort. The fake site pulls images and layouts from the real site, usually a bank or other financial institution, and passes the user's information back to the real site to mimic a regular log-in--while keeping a copy of the account data for the criminals.
The draw, of course, is ever-increasing profits. Research firm Gartner estimates that 3.5 million Americans gave up sensitive information to phishers in 2006, an 84 percent jump from the previous year--for a total loss of $2.8 billion. One single phishing gang, called Rock Phish, is estimated to have taken in more than $100 million.
According to security experts, Rock Phish has pioneered many of the techniques that have contributed to the recent jump in phishing sites. And the image spam that hides its pitch from filters by embedding it in a picture was a Rock Phish invention, these experts say. On some days this one group, which specializes in spoofing U.S. and European financial institutions, may account for as many as one-half of all the phishing sites in operation, according to researchers.
Heuristic scanning may help combat the scourge. Instead of depending on a blacklist of known phishing sites, it analyzes a site's behavior, looking for techniques commonly used by phishes. IE 7 uses heuristics, as does the free Site Advisor browser add-on for IE and Firefox.
An emerging standard for a new type of site certification--called Extended Validation Secure Sockets Layer, or EV SSL--may also help. To get this certificate, sites will have to be checked out by third parties like VeriSign or Entrust to make sure that they at least appear to be legitimate. On such sites, the browser address bar will turn green.
Microsoft supports EV SSL in its IE 7 browser, and major online-commerce sites such as PayPal have now started to come on board as well.
But if the current surge in phishing sites demonstrates anything, it's that phishes can and do get around automated tools and procedures to protect their sizable profits. Recently they have been developing new technologies that could well thwart protection measures like EV SSL Certificate, according to Aviva Litany, a Gartner analyst.
Litan, who doubts EV SSL Certificate will have much impact on phishing, believes security technology firms deserve some of the blame for the growing phishing threat.
"The security industry has been a little arrogant," she explains. "I don't think that people realize how sophisticated these [online] criminals are."
Best Defense
Although no magic bullet may exist now (or ever) to safeguard us all, there is one simple way to protect yourself from the majority of phishing attempts: Never click a link in an e-mail or on a third-party site to go to any of your financial accounts. If, instead, you always use your own bookmark or type in the address, even when you're 100 percent certain that the e-mail is legitimate, you should be safe.
Automated tools, such as the free Password Safe and PwdHash utilities can still provide help. But to combat ever-adapting phishers, your best protection remains...you.


Monday, 4 July 2011

GeoTrust again win and Beats Go Daddy in Battle of SSL Market Share


GeoTrust is again top of the SSL market share in top websites, according to the latest "Alexa Netcraft Index," a monthly research on Secure Sockets Layer (SSL) certificate used around the world.

In the Alexa index of GeoTrust, a primary SSL certificate authority (CA) secured 20.6 % of exclusive domains in the million most visited sites. The VeriSign is 17.9% of all exclusive domains. Go daddy again was third with 15.6% share.

The latest results show GeoTrust is repeated front in the high-volume; low-cost SSL market remains unchallenged. In this business market segment, low prices make purchase decisions in SSL customers whose main purpose is to encrypt data transferred to and from the sites. On the other side, the VeriSign brand go ahead the premium SSL certificate and online trust, where customers demand full business certification, seal-in-search, daily Malware scans, and other extended services in addition to encryption.

With SSL certificates issued in more than 150 countries in the world, GeoTrust offers outstanding SSL certificates with fast delivery at low value. Enabling up to 256-bit SSL encryption, they include a range of GeoTrust® True Site seals based on the preferred level of identity authentication.

If you do Transaction online, you are alert of the meaning of get a customer satisfaction to ensure they feel secure and able to complete the transactions. Best way to get the trust is SSL certificates. It is importance you trust on your SSL certificate vendor. Like GeoTrust is Top in the fulfilling of customer satisfaction so it is top in the battle of SSL certificate market share.

GeoTrust SSL certificate arrive with fast delivery a lowest price. Strong encryption, multi-domain support with extended validation options. When it comes to end users satisfaction, going with a reputed trade name is very necessary. GeoTrust is broadly popular respected to Go Daddy.

Warranty is also main factor of company. Incase if steal your personal information like Credit card information GeoTrust warranty ranges is $10,000 to $250,000 compared to Go Daddy’s $2000 warranty.

TheSSLstore.com is one of the largest SSL Certificates providers globally. Platinum partner forVeriSign, GeoTrust, Thawte and RapidSSL. Among the Internet security solutions TheSSLstore.com offers are SSL certificates from VeriSign, Thawte, GeoTrust, and RapidSSL. We buy SSL certificates in large quantities and pass the savings to you. To learn more about SSL Certificates visit
https://www.thesslstore.com

Tuesday, 28 June 2011

SSL Certificate Frequently Asked Questions

What is a wildcard certificate?

Security Risk:

Use of Wildcard SSL Certificates is strongly discouraged for most use cases. If possible try to make use of other certificate types such as multi-domain certificates. When you deploy a wildcard certificate and private key across multiple websites and servers, a single site compromise will result in the compromise of the entire sub domain. Also note that not all applications are compatible with wildcard certificates. In particular, many mobile applications will not work with wildcards.

Wildcard Certificates secure multiple subdomains with a single SSL Certificate. For example, you want to secure www.entrust.com, secure.entrust.com and support.entrust.com, you can use a wildcard certificate to secure all 3 sub domains under *.entrust.com.

There is a limitation on the way wildcard certificates work. This goes across the board for all Certificate Authorities. Wildcard certificates only support one level up in the fully qualified domain name.
For example, if we create a certificate for the common name of *.test.entrust.com, https://www.test.entrust.com/ will work; https://www.shop.test.entrust.com/ will not work. https://test.entrust.com will not work either.

When generating a Certificate Signing Request (CSR) for a Wildcard certificate, add an asterisk (*) to the left of the Common Name where you want to specify the wildcard.

What is multiple domain SSL certificate?

Multi domain certificate makes it possible to secure up to 100 domains on the same server with a single certificate. It is best for shared hosting environment. It must be reissued each time you want to add a new host/domain name to the certificate.

When generating a CSR for multiple domain certificate, enter the primary domain name in common name field. Let us know the rest of domain names you want to be included in the certificate.

What is Unified Communications Certificates?

Unified Communications Certificate is multi domain certificate specifically designed for use with Microsoft Exchange and Microsoft Office Communications servers.

What is Extended Validation Certificates?

Extended Validation EV SSL Certificates are the next generation SSL certificate because they work with high security Web browsers to clearly identify a Website's organizational identity. For example, if you use Internet Explorer 7.0, Firefox 3.0 or Opera 9.5 the address bar will turn green to identity this site as having an EV SSL certificate. A display next to the URL will toggle between the organization name and the certificate and the Certificate Authority that issued the SSL Certificate. The green bar means that a third party has validated the legitimacy of the business, the business' right to use the domain name, and the High- Assurance SSL Certificate was legitimately obtained.

Generating a CSR for EV certificate is the same as generating the CSR for a single domain SSL certificate.

Can I get a certificate for a host in a none cornell.edu domain?

Yes - as long as Cornell owns the domain. Send your request to Identity Management support.
To ensure the university's compliance with the InCommon agreement, requests for certificates outside of cornell.edu domains are subject to extra vetting and approval, by both the university and InCommon. To begin your request, send email to idmgmt@cornell.edu requesting the domain to be added, and IDM SSL admin will initiate the process of validating your domain with InCommon. After the domain is validated, you can then request a certificate for a host in that domain through normal channel.


Way to install SSL certificates safely


SSL Certificates are a way to ensure that your online information is all safe and protected. But you should carefully select the certificate and install it for your online business so that it functions efficiently.
Secure Sockets Layer or SSL Certificates are crucial to install when it comes to securing the online information on Internet. Today, all the reputable websites use these certificates to encrypt all bank details or personal details or from browser to server. This is done to ensure protection to all online purchases. However, as there are a variety of SSL Certificates, depending on the prices and your requirement of security, you should install them carefully

Know that each institution has its own security requirements. So, first assess your requirements and check them with your bank in case you accept credit cards and payments on Internet. At the time of choosing a secured SSL for your online business, do some research and know about different types of SSL. You should have the knowledge and distinct features ofdedicated SSL, shared SSL, SL encryption, Wildcard SSL and free SSL certificates. This way you can have more useful certificate.
There is always the requirement of a dedicated or unique IP address belonging to your company. This is because the SSL certificate should not be put on a shared IP address. There are very rare situations when the certificate is shared by two IP addresses
Another requirement is that you have to make a Certificate Signing Request or CSR. This you can do through your server control panel. This is also important to do if you are having such a certificate for the first time.
In order to install the secured SSL, there are some steps that you have to follow if you want to make the installing process easy and safe. First of all you should log on to your server. Then, next step is to generate a key in case you are applying for the certificate for the first time. Make sure that you include the http://www.homepage in your domain name.
Then, generate Certificate Signing Request. When you are given a choice, select with a www as it is most appropriate selection. You will be then asked some questions by the server. The CSR will be on display or emailed to you. You can copy the CSR on a notepad. This is done to copy all the random characters from beginning to end of the certificate request.
As a next step in installing of SSL certificate, you have to past the CSR on the field containing your and the vendor’s contact details. Select also an email address so that the signing authority can communicate with you through the address.
After the certificate is finally approved you will receive an email that looks a lot like a larger request form. You can then instantly install the certificate after pasting it on a field in the server. However, if you choose to upload the certificate from a text file, in that case the server will install the certificate.
If you follow these steps carefully, you are able to easily and safely install SSL certificate without any hurdles and problems. In case, you still find it harder to install and fail to do so, contact the service administration team to take the help.