Subscribe:
Showing posts with label SSL-Reseller. Show all posts

Monday, 15 August 2011

What Is The SSL Reseller Program?


Q. What Is The SSL Reseller Program? 

Answer:-The smartest way to earn more and do more with less effort and investment to zero. TheSSLstore you can earn as much running. Yes, we offer best VeriSign Resellers program for small business owners of web design, development and hosting company's site. Individuals, partners and leaders of commerce site can also sign up for SSL reseller program and start a new revenue stream.

Q. Why Should I Sign On Behalf Of Reseller SSL??

Answer:-Long growing world of online marketing allows you to earn more and more affiliates website, product resale and Google Ads. Our reseller program is not to invest money to register or activate. Our partners will receive the broadest offering SSL certificates to meet customer needs. Choose a full range of VeriSign, Thawte, GeoTrust, RapidSSL and products Trustwave. More than 20 products to choose from. All certificates you buy from us is exactly the same certificates you buy directly from VeriSign, GeoTrust, Thawte, RapidSSL and Trustwave. Choose a wide range of standard SSL Certificate, High Assurance certificates, certificates Wild, SAN certificates, EV SGC Certificates and Code Signing certificates.

Become a reseller today and immediately benefit the reseller control panel the most advanced ever. In your own customer portal:

* For certificates
* To monitor the automatic renewals and renewal
* Cancel Certificates
* Game Show History
* Communicate with customers via e-mail
* List of search warrants and complete and incomplete
* Receive account statements
* Analyze trends and data to better your customer base

Features & Benefits:-

1.       Best Pricing in the industry
2.       Best Service, support & technology
3.       Best selection for your all your clients’ needs
4.       FULL no cost API access
5.       NO sign up fees
6.       Most advanced reseller control panel to manage your SSL business
7.       Access to partner knowledgebase, educational tools & resources
8.       Easy payments via credit card, PayPal or bank wire
9.     Set your own prices while we remain anonymous, issuance of the certificate takes place in the vendors website
10.   Free to join Affiliate program with instant access to links and banners, real time statistics and one of the highest commissions in the web security industry

Wednesday, 27 July 2011

EV SSL - the antidote for SSLStrip attacks


EV SSL allows software to authenticate strongly in ways which defeat the SSLStrip attack. We saw that with conventional certificates, especially domain-validated certificates, there is no reliable information to back up the authentication of the domain name. To address this critical problem, certificate authorities and software companies joined to form the CA/Browser Forum4 and promulgate a new standard called EV SSL for Extended Validation SSL.

EV SSL defines rules for who can qualify for such a certificate and the procedures a CA must follow in order to validate the information. For instance, they must validate that the organization exists as a legal entity, that any organization names are legal names for that organization, and that the applicant is authorized to apply for the certificate.

EV SSL allows software to authenticate strongly in ways which defeat the SSL Strip attack.; see Figure for an illustration The fields in the certificate generally ignored by conventional SSL implementations, such as organization name, are required in EV SSL and can be checked every time. This second-level of authentication ensures that the parties know exactly with whom they are communicating. Since certificates contain organization names that have been verified, users and applications that rely on EV SSL Certificate can verify the actual owner of the certificate with confidence 


EV SSL enables software to authenticate strongly in ways which defeat the SSLStrip attack. In addition to the domain name, the fields generally ignored by conventional SSL implementations, such as organization name, are required in EV SSL and can be checked reliably every time. This second-level of authentication ensures that the parties know exactly with whom they are communicating.

The specification is also clear about the information that must be provided by the applicant. Other rules are more restrictive than with conventional SSL. For instance, wildcard certificates, the type that make null character attacks even more dangerous, are not allowed in EV SSL.

EV certificates are also limited in lifetime relative to conventional certificates: the maximum validity period is 27 months. This ensures “freshness” of the information in the certificate.

In addition to collecting a proper EV Certificate request, containing much organization information including the jurisdiction of incorporation, and a signed subscriber agreement, the CA is required to verify that the organization exists and operates at the locations specified in the request. They may go to government sources for this. They have to verify that the entity exists at the physical address they specify. For business organizations a face-to-face verification of the principal individual in the entity is required.
The requirements go on and on for 93 pages. It would be very hard to get a fake EV certificate.

EV certificates enable strong authentication

Standards also specify what software needs to do in order to authenticate a party based on a certificate. Unlike the loose conventions which developed around conventional SSL, these rules must be followed for EV.

When encountering an EV certificate, a program must confirm first that the CSP (Certificate Service Provider), meaning the certificate authority who issued the EV certificate, is authorized to issue such certificates. Each CSP has a unique EV policy identifier associated with it which must be compared to the identifier in the end-entity certificate.

Applications that use EV certificates properly need to embed CSP root certificates in order to confirm that certificates they encounter are issued by trusted roots. Required procedures for CSPs to work with application developers, including providing test facilities, are defined by the CA/Browser Forum.

“Relying applications [clients authenticating certificates] must provide adequate protection against malign threats to the integrity of the application code and the CSP root.” This is the sort of requirement that needs some history to fully-define itself, but basically it puts the onus on application developers to take care to write secure code.

The rules state that applications must be able to handle key strength of symmetric algorithms of at least 128 bits.

Applications are required to check for revocation of the certificate before accepting it. The application should support both CRL and OCSP, although OCSP is clearly the wave of the future and the only scalable approach. (In his presentation Marlinspike suggests a method for bypassing OCSP by returning a “Try again later” code, in which case the application typically gives up and authenticates. The EV rules state: “If the application cannot obtain a response using one service, then it should try all available alternative services.” This precludes the lazy behavior described by Marlinspike.)

Once all of these requirements have been met and the fields in the certificate match those expected by the application, then it may proceed.

Implementation considerations

Adopting EV SSL is not simply a matter of buying and using an EV SSL certificate. Client software has to know to look for an EV SSL certificate and to follow the rules for implementing EV SSL authentication .
Fortunately, it’s not difficult programming, but it needs to be done potentially with in-house as well as with 3rd party client software code. But the work is the same in all places. If you are well-organized about your certificates then it will be straightforward work. And many products, including current Windows versions, support EV SSL out of the box.

SSLStrip attack could be used against server-server communications with the potential for mass-compromise of confidential data

Advances in attacks on network security over the last few years have led to many high-profile compromises of enterprise networks and breaches of data security. A new attack is threatening to expand the potential for attackers to compromise enterprise servers and the critical data on them. Solutions are available, and they will require action by company officers and administrators.

“SSLStrip” and related attacks1 were among the highlights of the July 2009 Black Hat show in Las Vegas2. Researcher Moxie Marlinspike3 combined a number of discrete problems, not all related to SSL, to create a credible scenario in which users attempting to work with secure web sites were instead sent to malicious fake sites. One of the core problems described by Marlinspike is the ability to embed null characters in the common name field of a certificate, designating a domain name. This can be used to trick software, web browsers for example, into recognizing a domain name different from the complete field name. The result is that software, and users, are misled as to the actual domain with which they are communicating.

SSLStrip has not lacked for press coverage, but the analysis has focused on the consumer or end user with a browser. The use of SSL in embedded applications, including server-server communications, presents an even more ominous scenario. This is because SSLStrip attack could be used against server-server communications with the potential for mass-compromise of confidential data.

This spoofing problem is solved by proper use of Extended Validation SSL certificates for authentication. Moving certificate-based enterprise authentication to EV SSL would therefore protect an organization against this form of attack.

SSL authentication is most famous for providing secure web access to sites with sensitive information, such as banks, but it has many applications. It is commonly used, for example, as a means for parties in a machine-to-machine, typically serverserver conversation to verify each other’s identity; see Figure A for an illustration.

The recent revelation of a new attack against SSL threatens these server-server communications. An attacker who gains access to the network could use the attack to spoof the identity of a critical server and thereby gain unauthorized access to critical data.

Since EV SSL Certificates contain only authenticated organization information, businesses can employ EV SSL and require the organization information to match the expected values before allowing access to mission critical applications. In this scenario the intruder using the new attacks will fail to gain access because it will lack the presence of the EV certificate, the correct organization information, or both. 


It is possible to trick the client into seeing the name it expects, when the actual domain name in the certificate is that of a malicious site

The main weakness with conventional SSL certificates is that there are no standards for their issuance, nor any rules for what the fields in them are supposed to mean and which are required for authentication.One implication is that client applications, called relying parties, cannot have confidence that the organization listed as the owner of the certificate is in fact that owner. This follows all the way up the chain until the relying party reaches a trusted root.

In fact, the least expensive SSL Certificate, domain-authenticated certificates, don’t even authenticate an organization, merely an internet domain. Users can tell precious little from them about those with whom they are doing business.

Marlinspike’s SSLStrip attack demonstrated the combination of several attack techniques to exploit the above weaknesses and fool users / client applications into thinking they were using a trusted site / server, when in fact they were using a fake version of that site / server. He combined a number of techniques, including “man-in-the-middle,” fake leaf node certificates and the null character attack. 


Null characters in a domain name

The key threat Marlinspike discloses is the use of null (zero value, often designated ‘\0’) characters embedded in a domain name.

Online purchase of inexpensive “domain-validated” SSL Certificate is so automated that it’s often possible to buy one with an embedded null character. For example - \0thoughtcrime.org. In the attack, the domain name of the certificate is combined to the right of the domain name to be spoofed, for example, “www.verisign.com\0thoughtcrime.org”. (Thoughtcrime.org is a domain owned by Marlinspike and used by him in his examples.)

Most software treats the null character as a string terminator. So when SSL client software reads the certificate domain name in the example it will stop at the null and treat the certificate as valid for www.verisign.com as issued by the certificate authority.

Null-stripping

Two SSL implementations, the Opera and Safari browsers, defeat this specific attack by stripping null characters from the Common Name. Thus, in the example above, the comparison will be to www.verisign.com.thoughtcrime.org and it will fail. But Marlinspike claims that some certificate authorities can be tricked with the same vulnerability in a way that makes null-stripping itself a vulnerability. In his example, he buys a certificate for sitekey.ba\0nkofamerica.com. Presumably he owns nkofamerica.com. When this name is presented to Opera or Safari it will display his attack site as sitekey.bankofamerica.com, the login page for that bank.

Man-in-the-middle

If you’re on the same local network as the server you are compromising, Marlinspike’s techniques make it very possible to perform the man-in-the-middle attack; see Figure B for an illustration. A number of popular techniques exist for this: A rogue wireless access point is one, or DNS or AARP cache poisoning.If you’re not on the same network then you need to get there, which you can do most likely by installing malware on a relatively less-secured system on the same network. The attacks which make this possible are legion.

Damage potential in server-server environments

The damage potential of this attack in a server-server communication scenario, such as database servers synchronizing across a WAN, is substantial.

Such servers commonly use SSL to authenticate each other. A malicious user on the network could spoof that authentication using the techniques described above. One that authenticated as a database mirror could capture the entire database including, if it’s stored on the server, privileged information and confidential customer data.


Sunday, 10 July 2011

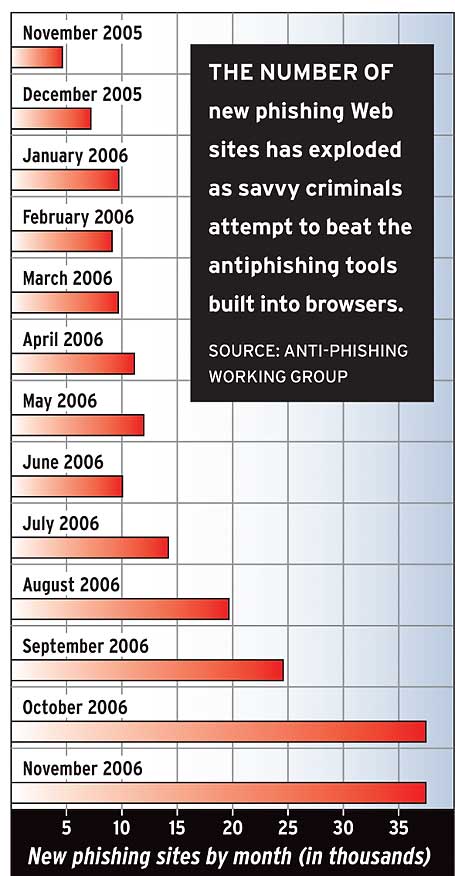
Phishing Sites Explode on the Web

Online criminals are thriving even in the face of new automated defenses.


Think the new built-in phishing filters in Internet Explorer 7 and Firefox 2 will protect your private data? Think again. The number of sites devoted to phishing skyrocketed last year, and the number of Americans taken in by phishing schemes has nearly doubled. In November 2006, the last month for which data is available, the Anti-Phishing Working Group found 37,439 new sites, up an astounding 709 percent from the 4630 sites in November of 2005. (Click on the "Image Enlargement" icon above to see the chart showing this trend.)
Last October, both Mozilla and Microsoft released new versions of their browsers that use blacklists to block access to known phishing sites. In response, resourceful phishes are flooding new fake Web sites onto the Internet too quickly for them all to be shut down or blacklisted.
The alarming ease, with which the fraudsters changed course, plus other new phishing tactics, makes some security experts say that phishes have the upper hand in the war against online fraud.
"Ultimately," warns Zulfikar Ramzan, who is a senior principal researcher with Symantec's Security Response Group, "technologies that rely heavily on blacklists are going to be useless."
Easy Phishing
According to RSA, a security vendor, hackers in January started selling a phishing kit that lets criminals set up very convincing fake Web sites with little effort. The fake site pulls images and layouts from the real site, usually a bank or other financial institution, and passes the user's information back to the real site to mimic a regular log-in--while keeping a copy of the account data for the criminals.
The draw, of course, is ever-increasing profits. Research firm Gartner estimates that 3.5 million Americans gave up sensitive information to phishers in 2006, an 84 percent jump from the previous year--for a total loss of $2.8 billion. One single phishing gang, called Rock Phish, is estimated to have taken in more than $100 million.
According to security experts, Rock Phish has pioneered many of the techniques that have contributed to the recent jump in phishing sites. And the image spam that hides its pitch from filters by embedding it in a picture was a Rock Phish invention, these experts say. On some days this one group, which specializes in spoofing U.S. and European financial institutions, may account for as many as one-half of all the phishing sites in operation, according to researchers.
Heuristic scanning may help combat the scourge. Instead of depending on a blacklist of known phishing sites, it analyzes a site's behavior, looking for techniques commonly used by phishes. IE 7 uses heuristics, as does the free Site Advisor browser add-on for IE and Firefox.
An emerging standard for a new type of site certification--called Extended Validation Secure Sockets Layer, or EV SSL--may also help. To get this certificate, sites will have to be checked out by third parties like VeriSign or Entrust to make sure that they at least appear to be legitimate. On such sites, the browser address bar will turn green.
Microsoft supports EV SSL in its IE 7 browser, and major online-commerce sites such as PayPal have now started to come on board as well.
But if the current surge in phishing sites demonstrates anything, it's that phishes can and do get around automated tools and procedures to protect their sizable profits. Recently they have been developing new technologies that could well thwart protection measures like EV SSL Certificate, according to Aviva Litany, a Gartner analyst.
Litan, who doubts EV SSL Certificate will have much impact on phishing, believes security technology firms deserve some of the blame for the growing phishing threat.
"The security industry has been a little arrogant," she explains. "I don't think that people realize how sophisticated these [online] criminals are."
Best Defense
Although no magic bullet may exist now (or ever) to safeguard us all, there is one simple way to protect yourself from the majority of phishing attempts: Never click a link in an e-mail or on a third-party site to go to any of your financial accounts. If, instead, you always use your own bookmark or type in the address, even when you're 100 percent certain that the e-mail is legitimate, you should be safe.
Automated tools, such as the free Password Safe and PwdHash utilities can still provide help. But to combat ever-adapting phishers, your best protection remains...you.


Monday, 4 July 2011

GeoTrust again win and Beats Go Daddy in Battle of SSL Market Share


GeoTrust is again top of the SSL market share in top websites, according to the latest "Alexa Netcraft Index," a monthly research on Secure Sockets Layer (SSL) certificate used around the world.

In the Alexa index of GeoTrust, a primary SSL certificate authority (CA) secured 20.6 % of exclusive domains in the million most visited sites. The VeriSign is 17.9% of all exclusive domains. Go daddy again was third with 15.6% share.

The latest results show GeoTrust is repeated front in the high-volume; low-cost SSL market remains unchallenged. In this business market segment, low prices make purchase decisions in SSL customers whose main purpose is to encrypt data transferred to and from the sites. On the other side, the VeriSign brand go ahead the premium SSL certificate and online trust, where customers demand full business certification, seal-in-search, daily Malware scans, and other extended services in addition to encryption.

With SSL certificates issued in more than 150 countries in the world, GeoTrust offers outstanding SSL certificates with fast delivery at low value. Enabling up to 256-bit SSL encryption, they include a range of GeoTrust® True Site seals based on the preferred level of identity authentication.

If you do Transaction online, you are alert of the meaning of get a customer satisfaction to ensure they feel secure and able to complete the transactions. Best way to get the trust is SSL certificates. It is importance you trust on your SSL certificate vendor. Like GeoTrust is Top in the fulfilling of customer satisfaction so it is top in the battle of SSL certificate market share.

GeoTrust SSL certificate arrive with fast delivery a lowest price. Strong encryption, multi-domain support with extended validation options. When it comes to end users satisfaction, going with a reputed trade name is very necessary. GeoTrust is broadly popular respected to Go Daddy.

Warranty is also main factor of company. Incase if steal your personal information like Credit card information GeoTrust warranty ranges is $10,000 to $250,000 compared to Go Daddy’s $2000 warranty.

TheSSLstore.com is one of the largest SSL Certificates providers globally. Platinum partner forVeriSign, GeoTrust, Thawte and RapidSSL. Among the Internet security solutions TheSSLstore.com offers are SSL certificates from VeriSign, Thawte, GeoTrust, and RapidSSL. We buy SSL certificates in large quantities and pass the savings to you. To learn more about SSL Certificates visit
https://www.thesslstore.com

Tuesday, 21 June 2011

SSL Certificates In VMware View Environments


An SSL certificate could be described as a data container that includes the identity of a computer, the public key and the digital signature of the publisher of the certificate. Certificates are used to confirm the authenticity of a website, or the the public key contained can be used to encrypt the connection between a client and a server.
Making no further action the View Server is using a self-signed certificate. When you open the website of the View Server it gives you a security warning back that states that the certificate comes from an untrusted source.
To use your own certificates that have been signed from a trusted Certification Authority (CA), you can use the keytool that comes with the view installation on the Connection Server. With this tool, you create a trust store on the View Server, where your certificates  can be integrated. Request a certificte from an authorized CA. This may be the CA of your company, or a third party such as thawte, VeriSign and GlobalSign. It is also possible to integrate already-signed certificates for your server. In the next section, you can read the entire process for requesting a certificate from the Microsoft Certification Authority. For certificates from other parties, please refer to their documentation.
Certificates are only used by Connection Servers which are having direct connections with the clients. If you are using the Security Server for connections the certificate is needed only by this server.
Companies that use the Active Directory as their directory service, also often use  the Microsoft Certification Authority for their security certificates. The following example explains the steps needed to apply for a certificate and then to integrate this in a VMware View Server. First, you must apply for a certificate from the CA. Use the Microsoft Internet Explorer on the View Server because only with this browser the import and export of the certificate works without problems. "Open the Internet Explorer and type the correct address of your certification server in the address bar."This should be <certificatesrevername.fqdn>/certsrv/.Replace the wildcard certificate server name with the computer name of the appropriate server and fqdn with the fully qualified DNS domain name. 

Apply for a certificate on the website and mark it as exportable. After the newly requested certificate has been approved you revisit the site with Microsoft Internet Explorer and install the issued certificate. The certificate will be stored in the local certificate store now and you can export it in a file from there. In Internet Explorer perform the following action.  Click on the Tools menu and select Internet Options." This will open a window where you can change the properties and options of your Internet Explorer. 

»Select content from the tab and then click the button labeled Certificates. In the following dialog you have to select the certificate of your server and then export it to a directory on your hard disk. It is important that you export the certificate with the private key in the PFX file format. Name the certificate i.e. as server.pfx. After that you’ve to export the certificate for the CA of your company in the file format X509.

After a successful export of both security certificates, the trust store can be created. You have to use the keytool application. To use the application you should first adjust the environment variables on your computer so that the keytool can run without using long file paths. Open a Windows command line on the View server and type the following command:
set PATH =% PATH%,% Program Files% VMware \ VMware View \ Server \ jre \ bin \

Then switch the command prompt to the  directory where you’ve saved the certificates. Using the exported CA certificate in the keytool you’ll now generate the truststore. Replace <ca-alias name> by the name of the Certification Authority and <ca-certificate name.ce> by the real name of the CA certificate.
keytool-import-alias-file <ca-alias name> <ca-certificate name.ce>-keystore truststore

The newly created trust store and the PFX certificate must be copied to the subdirectory \sslgateway\conf in the program directory of the VMware Server View. If there is no file namedlocked.properties in the directory you’ve to create it as normal text file with Notepad. Otherwise, you open the existing file and modify it with the following parameters.

keyfile = server.pfx
keypass = <secret>
trustKeyfile = truststore
truststore type = JKS
useCertAuth = true

Please ensure that you’ve the correct password for the certificate in the keypass parameter. Afterwards the View Connection Server service must be restarted. This can be done via the Windows Services Manager. Check the Windows Event Log and the View server log files underc: \documents and settings\all users\application data\ vdm\logs for errors. If the View Connection Server service is not strating, there might be an issue with the certificate or password.

SSL Top News & Offers Of VeriSIgn:-

Get 13 Months of VeriSign Secure Site Pro with EV Security Now for the Price of 12 Months with TheSSLstore.com

Buy or Renew VeriSign Secure Site Pro EV Security for 13 Months at TheSSLstore only.

Pricing:
VeriSign Secure Site Pro with EV @ $1199.00 for 13 months

TheSSLstore is a Fully Authorized Platinum Partner of the VeriSign Secure Site Pro EV SSL Certificate. TheSSLstore has an exclusive offer for VeriSign Secure Site Pro with EV SSL Certificates. Buy or Renew VeriSign Secure Site Pro with EV for 13 months @ $1199.00 with TheSSLstore.com.
Get instant access to this VeriSign Secure Site Pro with EV SSL exclusive offer:

https://www.thesslstore.com/verisign/verisign-specials.aspx

OR
https://www.thesslstore.com


Thursday, 16 June 2011

Embed strong authentication into mobile applications

To improve the speed and efficiency in which financial institutions develop and provide customes secure, trusted mobile banking applications, Entrust announces their Identity Guard Mobile SDK for mobile platforms. This security toolkit helps banks transparently embed Entrusts strong authentication technology into an organization's new or existing mobile-banking application.

From e-mail communication, social networking, banking, commerce, shopping and personal entertainment, mobile devices have enabled a radical shift in the manner in which organizations can now service their customers. But the growth in mobile devices and the drive to move more services to the mobile channel has also increased incidences of fraud targeting these devices.

The SDK also will assist financial institutions with deploying stronger authentication for online customer security, a requirement expected to be at the center of upcoming guidance from regulatory agencies of the Federal Financial Institutions Examination Council (FFIEC).

The organization's 2005 guidance took a strong stance in support of the deployment of stronge authentication methods, as well as fraud detection techniques, to protect customer identities and information during online banking transactions. But advances in criminal technology demands stronger guidelines to help stop advanced attacks that target the identities and transactions of consumers and business-banking customers.

Embedding OTP tokens is more cost-effective than purchasing, issuing and deploying hardwar tokens because it leverages devices that are already widely deployed — increasing user acceptance. This transparent approach meets mobile user expectations of quick, simple application access and helps application providers build a consistent brand between their mobile application and online presence.

For software developers creating mobile applications, security is often a secondary concern yet needed to help comply with regulatory guidelines for the financial industry, such as those provided by the FFIEC. But because of its straightforward APIs, the Entrust Identity Guard Mobile SDK allows developers to easily design and implement identity-based security into their branded mobile applications without sacrificing usability or transparency for end-user adoption.

The SDK provides a number of capabilities that enables features such as transparent strong mobile authentication, soft token display to address online banking security and out-of-band transaction verification to help defeat advanced fraud attacks such as man-in-the-browser. With support for the most popular platforms, the toolkit delivers a common API framework that allows developers to leverage integration efforts across multiple development environments.

TheSSLstore.com provide the EV SSL Certificate at discounts through its Platinum Partnership with VeriSign, GeoTrust, Thawte, and RapidSSL, offering SSL certificates at steeply discounted rates, 24/7 support, and a 30-day money back guarantee. TheSSLstore is one of the largest and most trusted SSL certificate providers globally, with clients ranging from NASA and IBM to thousands of small businesses.